More Time Wasters: I won’t beat around the bush. I know BOB is your password.

I got this in the early hours… and ‘BOB’ replaces what was actually a real password I have been using, that they somehow had grabbed…

The entire scam is automated generic trash of no real substance, but I was intrigued on how they had gotten hold of my username and a real password…


Subject: mak- BOB


I won’t beat around the bush. I know BOB is your password. More importantly, I do know about your secret and I’ve evidence of your secret. You don’t know me and nobody paid me to examine you.

It’s just your bad luck that I stumbled across your blunder. Actually, I actually setup a malware on the adult vids (sexually graphic) and you visited this web site to have fun (you know what I mean). When you were busy watching video clips, your web browser started out operating as a Rdp (Remote control desktop) having a key logger which provided me with access to your screen and also web camera. Right after that, my software program gathered your entire contacts from fb, and email.

After that I put in much more time than I should have exploring into your life and created a double-screen video. 1st part displays the video you were watching and next part displays the video from your webcam (its you doing inappropriate things).

Honestly, I want to forget all information about you and let you get on with your daily life. And I will provide you two options which will make it happen. The above choices with the idea to ignore this letter, or simply pay me $ 2900. Let’s explore above two options in more detail.

Option One is to ignore this email. Let us see what will happen if you take this path. I definitely will send out your video recording to your entire contacts including friends and family, colleagues, and so forth. It doesn’t help you avoid the humiliation your family will ought to feel when friends find out your sordid videos from me.

Second Option is to make the payment of $ 2900. We’ll name this my “privacy charges”. Now let me tell you what happens if you choose this path. Your secret remains your secret. I’ll delete the video immediately. You continue on with your daily life like none of this ever occurred.

At this point you may be thinking, “I’m going to report to the cops”. Let me tell you, I’ve covered my steps to ensure this email can’t be linked returning to me and yes it will not steer clear of the evidence from destroying your health. I am not trying to break your bank. I just want to get compensated for the time I place into investigating you. Let’s hope you’ve decided to produce this all vanish entirely and pay me my confidentiality fee. You’ll make the payment via Bitcoins (if you do not know this, type “how to buy bitcoins” in google)


Amount to be sent: $ 2900

Bitcoin Address to Send to: 1KjxgUYw2QC53ZiGeAG9uohcSSRUWsSsQA

(It is case sensitive, so copy and paste it)


Tell no-one what you would be using the Bitcoins for or they might not sell it to you. The process to get bitcoin may take a short time so do not put it off.

I’ve a special pixel within this message, and right now I know that you have read this e mail. You have 2 days in order to make the payment. If I do not receive the Bitcoins, I will send your video to all your contacts including relatives, colleagues, and so on. You better come up with an excuse for friends and family before they find out. However, if I do get paid, I’ll destroy the video immediately. It’s a non negotiable one time offer, so kindly do not ruin my time and yours. The clock is ticking.

Oh no’es, what will I do’es? My secret (eh?) is out. I am so glad they are not trying to extort me into bankruptcy and are asking for a reasonable fee so they can protect my secret for me and conceal my shameful behaviour from those I love dearly.

I am also glad for the ‘copy and paste’ tip! Phew! I would not have liked to mistype that Bitcoin address and mistakenly pay the wrong person.

And – yikes! – a ‘special pixel’! In a plain text email! How do they do this magic?

Sigh. Please note the sarcasm.

What secret? I don’t watch pron – truly – and my webcam USB is unplugged on my desk at all times, until such time I use audio/video messengers. I have never trusted that little beady glass eye with the blue light underneath it, staring at me silently. It reminds me of HAL 9000 too much. Also, the password in question hasn’t been used for my PC for about, oooh, six years?

If the email had been HTML, I may have been a bit wary of the ‘special pixel’- but even so I wouldn’t gave given a damn. Unless my malware and email defences failed me, I would remain ‘untracked’. Even if not, I was tempted to reply to them and ask them for a URL to the video they had of me watching pron. It would be entertaining to watch a film of myself doing something I had never done. It’s amazing what they can do with CGI these days!

I suspected they had compromised WordPress (for we know it’s a bit of a Barn Door), as I have used this password (too widely) in the past. Even though all my sites are 2FA’d, you can still no doubt find ways to sneak past the defences – probably even get the 2FA QR code – without even logging in. But, again, that password hasn’t been used on my WordPress sites for years.

Some digging shows they got the details from ‘leakedsource.com’ (now shut down) – a site hosting billions of leaked accounts/usernames/passwords from various site break ins. I’ve checked the Bitcoin address, it’s valid… and unbelievably 126 saps have fallen for this (so they probably do have something to hide and were too scared to take the risk, or – more stupidly – thought this was for real). The progenitor of this tosh netted over $120,000 USD!

Crime does pay, it seems.

Still, it did force my hand on a long overdue exercise. As I had used this same password widely years ago (I know, bad practice), I have long been meaning to clean up my act using a password manager to spot and change vulnerable passwords like they one they found… so 120 password changes later, that old password is a deader. Still, none of the ‘important stuff’ was involved, fortunately. And I’ve still yet to go through another 300 slightly more secure but still vulnerable passwords… more sigh.

I am tempted to ‘Request Payment’ for $120,000 from the Bitcoin address just for a larf… for ‘reciprocal privacy charges’… or perhaps as payment for my time being forced to update my sloppy password usage 😀

Still, a safe outcome – this time… it could have been much, much worse! and a clear message that even if you do know the risks of data compromise/insecure passwords (as I definitely do!), and know you have to clean them up – it’s no good leaving that exercise until it’s too bloomin’ late!

If they’d actually tried to use the username/password against whatever service it was leaked from – they may actually have obtained data worth while – such as physical address, partial visa card details, what size underwear I use… and so on!

Good job they are thick, eh?

Though, not so thick as to having extorted $120,000 USD from some gullible/guilty people!
Bad Design: Costa Coffee Vending Machines

In ‘Victor Meldrew‘ Mode, which is all too often these days, I have come across the ‘one too many’ problem of sheer idiocy demonstrated in mass market design solutions, and decided that it might be time for a new blog theme: Bad Design.

The instigator of this line of thought, and therefore intended victim of it’s focus, is Costa Coffee, and my observation of the ‘ridiculous’ design points (read failings) of the vending machines they distribute throughout the UK retail space for franchises, supermarkets, and so forth.

Of course, as a professional Software Engineer, it is not sufficient to simply analyse and report problems, but I must also provide constructive solutions, and this I will do!

The Scenario

This morning, as is our wont, after walking our dogs we stop for our regular(ish) coffee hit. Now don’t get me wrong, Costa Coffee is ‘Costa’… not the best, not the worst, but ok enough.

After recieving my Caramel Cappuccino (thankyouverymuch) and forcing me to ‘rate’ it out of 5 stars before allowing me to request the next drink, it began dispensing my wife’s normal Cappuccino.

One squirt of hot water into the dispensation, and it began emitting an ear piercing regular beep every second, then promptly stopped dispensing. This high decibel beep did not however.

It went on. And on. And on.

The staff in the shop were helpful, but had no idea what was wrong so had to open the machine. This resulted in several of the small, regular and large cups being forcibly ejected from the front of the machine, as the entire front opens as a door, a door through which the cup ‘poppers’ operate.

The already ear piercing beeping now doubled in volume. And would not stop. The machine had coffee beans in the full grinder. It had milk. It had half-filled bags for all the syrups it supported. It had water supply. It (obviously) had power. Yet still the beeping, which led to myself and the bemused shop assistant having to shout at each other to be heard between winces at the ear drum pounding beeps.

At length, I was had no choice but to depart with just my own coffee, tinnitus, sore ear drums, and a slightly miffed, coffee-less, wife.

Bad Design: Analysis

1) Ear Shattering Beeping Noises

WTF? Ok, beeping is useful, if there is no other medium to communicate errors (I’m coming to that). However, painfully loud noises in the work place are a Health and Safety violation, and I’m pretty sure from past experience that this beep definitely breaks the UK regulations on noise in the work place. That beep will definitely lead to hearing loss.

Solution: Quieter beep please. No expense required, and in fact saves electrical energy. FTW

2) Stupid Door Design

Opening the door requires you to remove all (ALL) the cups from the ‘poppers’? Really? Is this the work of an imbecile?

Solution: Do not create ‘work’ (removing the cups first, or tidying them up afterward). Instead, hinge the door so the cup ‘poppers’ are not part of the door itself. Perhaps slightly more expensive per unit, but come on…

3) Failing to provide a meaningful error

THERE IS A TOUCH SCREEN ON THE MACHINE! Here’s an idea! Why not display an error message?? Like “123: Out of Milk” or “234: Grinder Jam” Clearly the machine can detect the error and BEEP loud enough to deafen someone, so clearly it can use the sophisticated display medium to show a bit of meaningful context!

And yes, the touchscreen itself may fail, so having a beeping error code is just fine and dandy in tandem. But see point 1!

Solution: Use the hardware you already have! And get software engineers that actually know what they are doing. Probably more expensive, as you pay for what you get. See maksw.com for a recommended software provider 😉 A one off extra cost for software divided by all machines which use it (so almost zero cost), and probably one extra bit of wire in each machine.

4) WHY FORCE CUSTOMERS TO RATE A VENDING MACHINE?

Why? Are Costa really that insecure that they can’t just use vending statistics to see how popular their machine is?  Does the vending machine have emotive AI and I may hurt it’s feelings if it serves me excellent, piping hot coffee and I fail to rate it highly before walking away? Does it post my rating to social media to show it’s friends how good it is and how much people like it?

Why must I rate it to order another drink?

I thought these vending machines were for ‘fast service’, but no, instead the queue of people behind me have to wait while I ‘rate’ my vending machine for the dispensation of a coffee… that’s those that can still hear after being deafened by the beeping, and can be bothered to wait for someone who has no clue how to diagnose mystery, unknown errors which the machine knows about but won’t reveal and somehow fix it so the queue of customers can get a coffee and be forced to rate it ‘1 star’ for making them wait and being deafened.

Solution: Rating a vending machine? Really? Remove this stupidity. Cheaper.

5) Sugar/Chocolate Dust/sachet ‘squirrel holes’

Ok, this is just nuts (pun intended). One hundred or so packets of sugar, or chocolate, that are pesky little shiny paper beasts and do not ‘stick’ to anything… then put them in a horizontal container without an ‘end’ so that they form an unstable pile. Then expect someone to remove just one of them.

It’s like playing Jenga with blocks of oil coated teflon instead of wood. Remove one sachet in the barely stable pile, and they all start slipping about and (if unlucky and the pile has been stuffed by an over-enthusiastic shop assistant) you get an avalanche of sachets which – fortunately/unfortunately – largely end up in the rubbish bin hole directly underneath. Great ‘waste’ of perfectly usable sachets there.

Solution: Angle these containers so the back of the container is lower than the ‘entrance’. Miniscule cost option, cost saving by removing the loss / waste of avalanched (made-up-verb) sachets going in the bin.

Summary

There you go. A much improved customer AND franchise store experience, for almost NO extra net cost. Amazing.

Costa! and all vending machine manufacturers! Pay heed!

🙂

The Beauty of Apple Swift Emojicode…

Swift (and to be fair other languages) supports unicode characters within the language. It sounds a reasonable feature; to allow non Latin-1 characters to be used, such as Kanji. After all, why should a native Japanese developer be forced to name variables, classes, methods et al using a predominantly English character set?

But, unicode supports far more than just language oriented characters, and in the hands of – shall we say – more playful software engineers, there may be trouble ahead… you could possibly expect to see code like this floating around the detritus of the crap-ladden shores of the grand interwebnet…

And remember, this code compiles and runs…

Let’s create a class object definition; (apologies for the line spacing, WordPress simply doesn’t care.)

class ?

{

    private var ? = “”

    private var ? = false


    init(?: String)

    {

        self.? = ?

    }


    func ??() -> Bool

    {

        //  ? likes Charlotte’s Web! Some ?!

        return true

    }


    func ?(?: Bool) -> Bool

    {

        // ? likes ?s so if given one, ? eats it

        if(?)

        {

            ? = ?

        }

        return ?

    }


    func ?(?: Bool) -> Bool

    {

        // ? does not like ?!

        return false

    }


    func ?() -> Bool

    {

        // is ? full?

        return ?

    }

}

“What the?” you may ask. No, dear reader, your eyes do not deceive you. All those cute little emoji’s are correct, and not code characters mistranslated by WordPress.

We can indeed create a ?(pig) class, and ask it if it likes bacon with func ?(?: Bool).

Now let us say we want to breed some ?s… a Pig Factory object would be useful…

class ??

{

    static func ??(?: String) -> ?

    {

        let ?? = ?(?:?)

        return ??

    }

}

And of course, now we can ‘breed’ pigs, we need a farm to manage them, and feed them (provided they like Charlotte’s Web, of course)… one hundred pigs should just about do the trick…

class ?

{

    func ???()

    {

        let ?? = 100


        var ?? = 0


        while(?? < ??)

        {

            let ?? = ??.??(?: “Bob”) // every ? is called “Bob” as they probably don’t answer by name anyway


            if ??.??()

            {

                if !??.?()

                {

                    if(!??.?(?:true))

                    {

                        _ = ??.?(?:true)

                    }

                }

            }


            ?? = ?? + 1

        }

    }

}

And finally, for irony’s sake, we’ll use some clear English to get our farm to create some pigs…

        let farm = ?()

        farm.???()

I can tell you, stepping through this in debug to make sure it ran, was a pure joy… while the code runs and does indeed create ??s, Xcode’s debugger simply would not have any of it, and jumped around like a crazed kangaroo on acid. Nice. I wonder what kind of experience our Japanese colleagues have trying to debug their natively named methods…

Glibness aside (and above is very glib!) there is value in supporting unicode ‘in language’, however, Apple, please restrict it to actual ‘text’ language instead of stupid symbols? Naturally, allow anything inside string objects or quotation marks as you may validly want to display them in UI, but for the actual code itself, text only! Also, try actually testing that all the toolchain supports them? Like, say, the debugger? Slightly important, not too easy to miss… really. I can only hope that actual software engineers can resist, and if they can’t that whoever’s reviewing their code uses a damned big stick to smack the emoji’s back into real text.

As an aside, apparently Apple did ban all the unicode line/border characters to stop developers drawing unicode art boxes around everything in their code. So they clearly realised this would be abused by someone.

Several steps too short, yet again Apple… though who cares, really, right?

Microsoft Windows 10 Creators Update: FAIL

Seems Microsoft (who have long been winning back my respect) are slowly tipping over sideways…

I have the (genuine) pleasure of owning a Microsoft Surface. I updated it with Windows 10 Creators Update.

I then experienced horrifically (unusable) slow applications, including Explorer, which lethargically drew their windows in almost line by line it seemed. I checked Task Manager, and saw it was hitting 50% + with the System Services, and high internet download bandwidth. I ‘presumed’ (because Windows was not telling me) that it was downloading even more updates in the background still. No doubt to fix other as yet unseen W10CU problems.

So I left it. For four hours.

After it had dropped to 0% CPU, I ventured to restart the laptop, and it did indeed seem a little better. But not much. I then noticed that certain operations (like doing a search in Visual Studio) resulted in the full screen window ‘resizing’ to be almost square, distorting the pixel aspect ratio within the window, and leaving a wide black strip down the right hand side of this new ‘internal’ window. Ultimately, it froze the application, forcing me to ‘End Task’. This happened on numerous other applications as well, so I’m guessing it’s a windows display driver issue, or the internal window framework getting itself in a twist.

I chose to resolve this.

Start / Settings / Updates & Security / Recovery / Go back to a Previous Version of Windows – Yes, please.

Fortunately, it seems Microsoft did get the roll back system right, as now I’m back to Pre W10CU, and amazingly, everything works just fine and dandy.

Frankly, I’m astonished their ‘highly promoted and awaited’ CU updated doesn’t work on their own hardware.

But, the journey does not stop there, dear me no.

Being a sado-masochist (apparently) I also updated my desktop PC (a custom built workhorse).

After updating, I was amazed to find the display at half brightness, and all colours desaturated to the point of greyness. I tried in vain to adjust my nVidia settings, and then discovered that the ‘Brightness’ option in Windows has been removed. After much googling which provided no answer I was happy with, I then chose to resolve the problem myself.

Start / Settings / Updates & Security / Recovery / Go back to a Previous Version of Windows – Yes, please.

Phew. Everything back to normal.

So, +1 for a robust and reliable version rollback!

But about -100 for a crappy version release.

Frankly, shocking. Ok, so apart from the crappy performance, none of the above are major issues. But, they are major usability issues, and frankly, I’m amazed Microsoft let this one out of the box.

Are the days of Windows Vista about to return to plague us all?

Microsoft Outlook 2016 FAIL

(slaps-self-in-forehead-in-amazement)

I can’t believe – with the modern day cross platform distribution of data – that Microsoft’s latest Outlook 2016 does not support synchronising with Google Calendar or Google Contacts!

It does provide some kind of crummy ‘view only’ sync with Google Calendar, but forget changing anything as it will only appear in your local calendar on that device – that’s great ‘cloud data’ that is!

But wait! What’s this? Windows 10 ‘Mail’ and ‘Calendar’ and ‘People’ apps do support Google Mail, Google Calendar and Google Contacts!

??????

So the crappy (but free) ‘get you by’ apps support what I want.

But the professional ‘I pay a lot of money each year to subscribe to Office 365’ software, does not?

??????

Am I missing something here? Clearly I am, it’s called ‘common sense’. Get off your high horse Microsoft, and fix this!

Out of (let’s face it, less than ‘desperate’ desperation) I configured Mail, Calendar and People just so I could at least see my Google data. It worked!

Until the first sync that is. ‘Account settings are out of date.’ Eh? Ok… ‘Fix account’… Yes.

No.

Repeatedly.

No.

It seems it cannot handle Google 2FA even though it did ask to set it up. Every time I ‘Fix Account’ I get hit with 2FA again, despite clicking ‘Do not ask again on this computer’. Every. Single. Time. Turning off 2FA is not IMHO an option. I am not going ‘less secure’ because Microsoft are shite.

I then turn to ‘Open Protocol Connector’ which adds CardDAV and CalDAV support to Outlook. After all, both have only been widely accepted standards for what, a decade? Why should Microsoft bother with them?

Fortunately, my domain host provides CardDAV and CalDAV. So, once configured, all I  have to do is migrate my Google stuff to my domain host. Annoying, slightly, but not really that big an issue.

Except of course, that after configuring Outlook using the OPC for my domain server, it can’t confirm all the services Outlook needs to use, so basically won’t set up.

I then uninstall the ‘Open Protocol Connector’.

Another option is ‘Google App Sync’ which – apparently – does work. And why? Because you have to pay for ‘Google for Work’ in order to use it.

Ah. Now I see. Microsoft do not support Google API’s, and Google charge you for the privilege of being able to add support.

A joint Microsoft / Google conspiracy to generate more money for Google?

Whatever next?

Swift

Of late I’ve been turning to (finally) learning the Swift language developed by Apple, notably for their iOS platform.

The Swift language is now on version 3.0, and by now should have settled down, ironed out all it’s kinks, and generally matured.

Wrong-o.

I’m not a ‘hater’ – I have written software in some many different platforms, languages and IDE’s that I’ve honestly lost count. I don’t mind learning something new, or adapting to changes. It’s a requirement for a professional software engineer.

But so far, Swift 3.0 ain’t mature. Far from it in fact. Now, to be fair, I do like it – mostly. The syntax is a lot cleaner than Objective-C, and yes it does seem to be easy to pick up, especially knowing how iOS frameworks and components already work, and being able to mix .swift with .m/.mm is awesome, as is being able to mix .c and .cpp.

But, there’s a but.

This ‘cleaner’ syntax rapidly turns into a mess of optionals (?) and down-casting (!), and means a double-meaning to established ‘c’ like operators.

if(!weekDays[eventDay! -1])
{
   // do stuff
}
var dictionaryYearWeekDayEvents = Dictionary<Int, Dictionary<Int, Dictionary<Int, [Event]>>>

I mean, wtf? I smell C++ Templates… and this is the structure I want, but now with Swift Dictionaries I am forced to specify the entire object structure before I can use it. NSDictionaries in Objective-C allow me to do it ‘whenever’. Ok, a double-edged sword I agree. Swift is better in the regard that it has tighter constraints on typing objects which is definitely a win. This is a programming paradigm I have to adjust to in my own head.

I also don’t quite get the concept of ‘optionals’;

var someObject: ObjectType?

Ok, so this means ‘someObject’ may not actually exist, i.e. will be nil. So then why does Swift throw an exception if the optional is nil when I try to use it in my own code which allows it to be optional?

Now granted, I am no Swift expert, of course! I’m just starting, but the above are examples of what the language let’s you do. It’s no better than C giving you the rope to hang yourself and C++ tying the noose for you and providing the stool.

Swift’s language spec and syntax makes it incredibly easy to get yourself into a nasty place, very quickly indeed. Not quite what they had in mind with the name ‘Swift’ I’ll warrant. I foresee a lot of domain expert knowledge being consumed by engineers being needed to clean up a lot of messy code in the future, now that enterprise applications seem to finally be taking off on the iOS platform, and all the new gig’s are ‘Swift’ based.

They also changed the majority of the API stack for Swift 3.0, compared to previous versions. This is bad, and strongly hints at a major and fundamental underlying flaw in the original language spec. This may have been something I’d expect to happen say in Swift 2.0, but not afterwards. The language should have been firmly locked down beyond 2.0

This has led to a lot of confusion on the internet with many ‘How do I do X in Swift’ examples being made instantly worthless (ok, the price of change I guess) but also with now examples given in Swift 1.0, Swift 2.0 and Swift 3.0. Worse, often the examples in Swift 3.0 no longer work –not because the authors are idiots, but because the example has been made redundant by even more changes since it was written.

Try figuring out how to sort a Dictionary by it’s key values. I dare you. I’ve given up. I just pull the keys out into an array, sort that, and then pull the dictionary items out in the sorted array order. It’s just less painful.

And then there’s Apple’s own documentation. Woefully poor for Objective-C but liveable. However, for Swift 3.0 it’s dire and nearly inadequate, often with contradictory examples, or no examples at all (ne. Sorting a Dictionary by key).

If all the above applied to Swift 1.0, I’d forgive, and put-up-and-shut-up. But for all this to be said at Swift 3.0, that’s just plain rude Apple, and shame on you for making the developers lives harder. Let’s not forget just who it was that actually made your mobile platform the place to be all those years ago…

Packaging Rant – Stop it! Just Stop It!

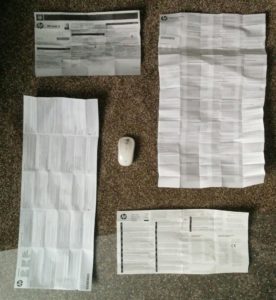
In this age of environmental concerns, it drives me nuts when I purchase something and end up with something like this…

What the…? Why oh why do I need all this paperwork printed out for a wireless mouse for heaven’s sake? Hewlett Packard, shame!

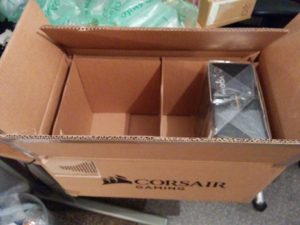
Then I ordered a pair of Corsair headphones, and this is the package that turned up…

Were there other items in this box? NO! Just those large air-pockets used to pack out the box. This is ridiculous, not only the waste in materials, but the delivery cost for the box.

So so what? Small peanuts compared to China’s fossil fuel glut, or our past atrocities (Industrial Revolution anyone?) but now multiply this stupidity by several billion other packaged items…

Little Men become Big Men, or Empower Them

That probably sounds a little trite, but the context here is ‘games developers’ and indies vs the rest of the world.

I read this Games Industry article with interest…

It’s not that ‘mobile has become hostile’ to indies. The problem is getting any market-space to get sales traction for the indie game developer. Now the big boys are in, it’s impossible. And now Apple have provided ‘ad space for sale’ it’s made it 100x worse, as the big boys just buy all the ad space. Purdy dumb move IMHO. Great for cash generation though!

It’s not the first time this has happened and it won’t be the last. Indies create the platform, because they are typically the first to embrace a new technology ‘because it’s cool’ or because it’s cheap/easy, etc.

iPhone was a desolate wasteland for games – Apple totally misunderstood their product for this genre, and took years to catch up. But by the time they did, the platform had been well established as a gaming hot spot by ‘the little men’, and it then attracted the attention of the big boys, who then dominated the top 20 from there on in. Only the really rare ‘stand out’ indie games made any headway. Nowadays you have to be the top 1% to get any revenue of note.

It doesn’t always work that way though – the GamePark 32 (which was awesome btw!) disappeared. The Raspberry Pi is doing well – but not stupendously so as it truly deserves – though again it’s a slightly different market niche.

So for the wannabe indie, there are two things to watch out for;

  • Hot new platform which none of the big boys support or care about (yet)
  • Big name behind the platform, or one who doesn’t understand the potential so hasn’t yet attracted the big boys

Get those two right, and get in early… and you never know…

Hmm… VR headsets anyone?

Mail Hackers are Pointless, Timewasting Muppets

Period. This is the second time this year I’ve had to deal with some bored sexually frustrated dullard f’baring my servers… earlier it was WordPress, which I had to secure up to the gills (hopefully!). Now it’s my email…

Today I suddenly started getting MAIL DELIVERY FAILURE NOTICE emails, initially a dozen or so… for emails I had not sent, and after reading some of the email address, to email accounts I’ve never heard of, and on reading the content… certainly with no content I’d ever send. It was all highly profane and offensive in nature.

Before I knew it, I’d got 103 email notices for emails I’d apparently sent to people whose accounts no longer exist. This means that far more had been sent to legitimate emails addresses. I shudder to think how many.

Fortunately, my domain hosts (unitedhosting.co.uk) responded within a minute of emailing my concern – they are very hot off the mark for all support calls. They checked the logs and found the password to my email account had been compromised (guessed) despite being non-obvious, mixed-case and alphanumeric – thankfully though this was easy to remedy.

So to the pathetic waste of DNA that thought spamming countless others with profane, offensive and highly inappropriate crap using my good name to do it, go $”^# yourself. No doubt I’ll be explaining & apologising to hundreds if not thousands of people should they choose to (quite rightfully) take umbrage.

One more thing on the list of ‘Too Many Things…’ only one I’d never have chosen and frankly resent having to do.

Thanks for wasting my life, and theirs.


Visit the awesomeness ofDominium!